Ing. Calogero Bono
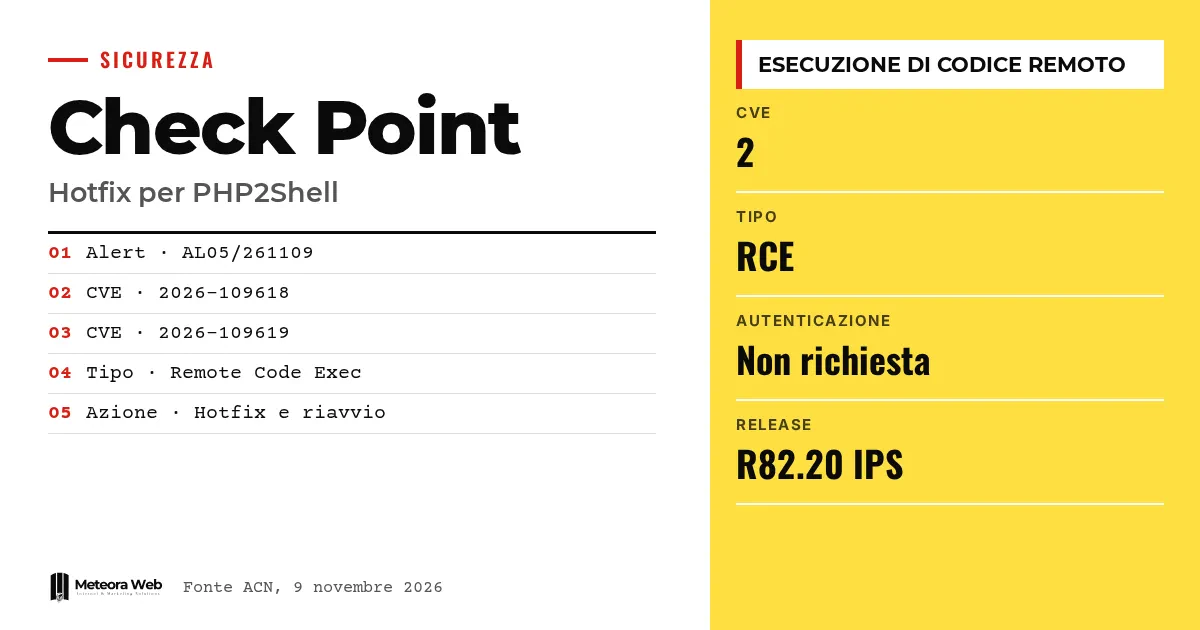
On November 9, 2026, CSIRT Italia, at ACN, published alert AL05/261109 on Check Point updates for the critical vulnerabilities known as PHP2Shell. They affect Firewall, Cloud Firewall, Security Gateway and Spark Firewall. An unauthenticated remote attacker could run arbitrary code on the device. It matters because these are perimeter appliances, the ones that are supposed to protect a company's network.
A few terms, before we get into the facts. PHP2Shell is the name given to two vulnerabilities, CVE-2026-109618 and CVE-2026-109619, in the PHP runtime built into the products. Remote Code Execution means running commands on the device from a distance. Hotfix is a fix released by the manufacturer for a specific version. EoS indicates a version out of support, for which the vendor may not release fixes. IPS is the system that blocks traffic considered malicious.
What did ACN report on PHP2Shell?
The ACN alert follows three earlier communications on the same vulnerabilities (AL07/261021, AL01/261025 and AL10/261028). Now Check Point has published a bulletin on the impact on its products, with hotfixes and mitigations.
According to the vendor, exploitation goes through requests crafted for the web interfaces exposed by the devices. ACN also notes that technical information on the exploitation is publicly available, which is why it asks for timely action.
Which products and features are affected?
The products affected are those that use at least one of these features.
- Mobile Access Portal (not for Spark)
- Remote Access VPN with SSL Network Extender (not for Spark)
- Remote Access VPN with SAML Realm authentication enabled
- Identity Awareness Captive Portal enabled
- UserCheck Portal
- Zero Phishing
For Firewall, Cloud Firewall and Security Gateway the versions are R81.20, R82, R82.10 and R82.20, plus several EoS releases from R80 to R81.10. For Spark Firewall the versions are R81.10.x and R82.00.x, along with R77.20.x and R80.20.x out of support.
What is not vulnerable?
Check Point has specified that Security Management Server and Log Server are not vulnerable. The same applies to the Check Point Portal and SaaS services, already updated. The vendor also stated that its products are not affected by vulnerability CVE-2026-115560.
Those who use only these components, or none of the listed features, therefore have a different exposure. It remains to be verified appliance by appliance, because the list depends on what is active.
How are hotfixes and mitigations applied?
ACN, in line with the vendor, indicates these steps.
- Install the hotfix for your version on all affected systems.
- If you previously applied the manual mitigation, first remove the changes to the file $CPDIR/web/Apache/conf/cp-httpd.conf.
- Restart the appliance at the end of the installation.
- If you cannot update right away, use the temporary mitigations in the "Mitigation" section of the bulletin.
R82.20 versions have built-in protection, the IPS "PHP Remote Code Execution", which Check Point says is effective even without HTTPS Inspection and without enabling the IPS blade. It does not replace the hotfix, however.
Limits to know
The ACN alert summarizes the vendor's bulletin and does not describe attacks observed in Italy. We do not know how many appliances are exposed. For EoS versions the vendor may not release any hotfix, so for those systems the picture may change. The detailed instructions should be read in the Check Point bulletin, which is not among the sources consulted here.
What changes for those working in digital
If you manage corporate networks or oversee their management, the first thing is to know which version runs on your firewalls and which features are active. VPN and Captive Portal portals are often exposed to the internet by design. For those who look after managed servers and hosting the issue is the same – update quickly whatever is reachable from outside. The case also recalls Fragnesia, under attack together with PHP2Shell. If an appliance is out of support, its replacement must be planned.
Our take
The most uncomfortable fact is the list of EoS versions, many and old. A firewall forgotten in production for years is a risk no hotfix can solve. It also weighs that the vulnerability sits in an accessory component, the PHP of the web interfaces, and not in the filtering engine. People often think of the firewall as a monolithic block, while it has management and access surfaces that need attention. Security vendors should make them less exposed by default.
Frequently asked questions
What are the PHP2Shell vulnerabilities?
They are two critical flaws, CVE-2026-109618 and CVE-2026-109619, in the PHP runtime built into some Check Point products. They could allow an unauthenticated remote attacker to run code on the firewall.
Which Check Point products are affected?
Firewall, Cloud Firewall, Security Gateway and Spark Firewall that use features such as Mobile Access Portal, VPN with SAML, Captive Portal, UserCheck or Zero Phishing. Security Management Server and Log Server are not reported as vulnerable.
What should I do right away?
Install the hotfix for your version and restart the appliance. If you cannot, apply the temporary mitigations from the Check Point bulletin. If you had already applied the manual mitigation, remove it before the hotfix.
Is R82.20 already protected?
It has built-in protection, the IPS "PHP Remote Code Execution", which the vendor says is effective even without HTTPS Inspection. It does not replace the hotfix, however, the ACN specifies.
What about unsupported versions?
For EoS versions the vendor may not release any hotfix. In that case the temporary mitigations remain and, in the medium term, the move to a supported version.
What to check in the coming weeks on exposed firewalls
The alert is the fourth ACN communication on PHP2Shell, so the story is not over. It is worth following its developments.
- Check whether ACN publishes new updates to the alert, since there have already been three.
- Verify with your supplier whether the EoS versions in use will get a hotfix or should be replaced.
- After the hotfix, check that manual changes to the configuration file have been removed and that services work.