
 Ing. Calogero Bono
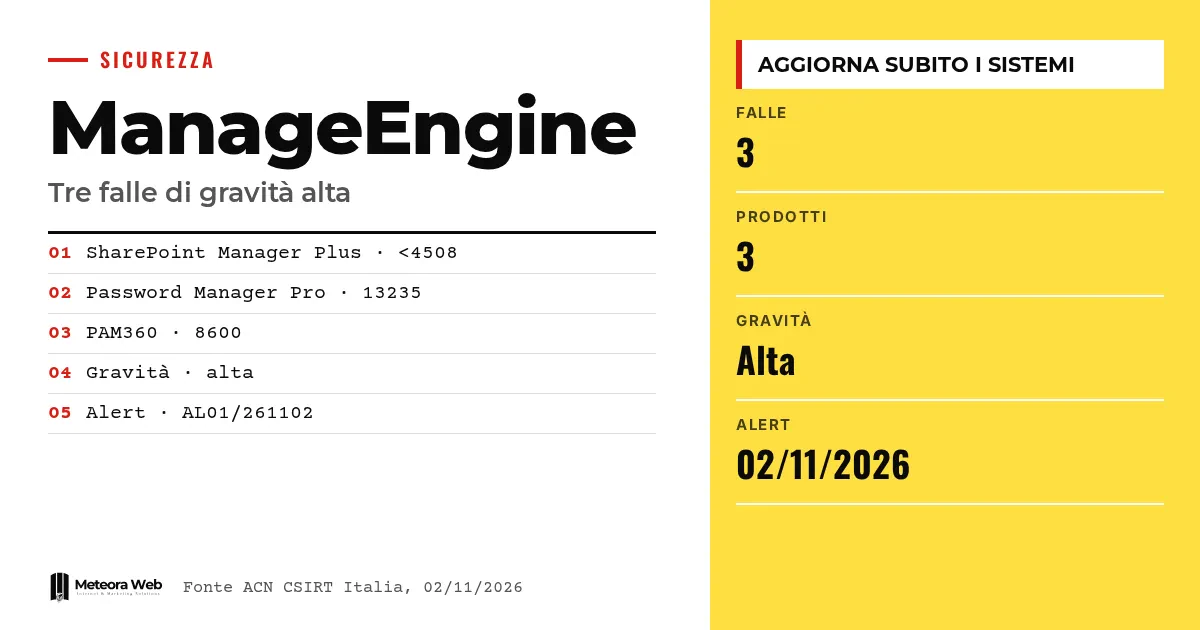
The CSIRT Italia, a unit of the National Cybersecurity Agency, published on 2 November 2026 an alert about three high-severity vulnerabilities in Zohocorp's ManageEngine products. The products involved are SharePoint Manager Plus, Password Manager Pro and PAM360. The last two store credentials and administrative access, so a problem there weighs more than elsewhere. Updates already exist and should be applied.
A few terms before we get into the facts. CSIRT Italia is the group that issues alerts about cyber threats in the country. Remote Code Execution means an attacker can run code on the system from a distance. PAM refers to privileged access management, that is, accounts with administrator powers. Denial of Service is the blocking of a service. Tampering is the manipulation of data.
What did the ACN report about ManageEngine?
According to the alert AL01/261102/CSIRT-ITA, the security updates fix three vulnerabilities rated «high». The alert describes SharePoint Manager Plus as a solution for managing and monitoring SharePoint environments. Password Manager Pro and PAM360, on the other hand, are platforms for credentials, privileged accounts and administrative access.
The notice is version 1.0, published on 2 November 2026.
Which versions are vulnerable?
The ACN lists these affected versions.
- SharePoint Manager Plus, versions prior to 4508.
- Password Manager Pro, version 13235 and earlier.
- PAM360, version 8600 and earlier.
If you use one of these builds, you are on the list. The fix for SharePoint Manager Plus is in build 4508, as the vendor's references indicate.
What kinds of attacks do they make possible?
The alert lists five types, Remote Code Execution, Denial of Service, Tampering, Information Disclosure and Security Restrictions Bypass. The summary does not say, however, which type corresponds to which product.
For this reason it is wise to treat all three platforms with the same urgency. In particular, remote code execution on a tool that holds privileged passwords is a scenario to avoid. For other recent cases you can read the scans on the Oracle E-Business Suite bug after the patch.
How do you secure the systems?
The ACN, in line with the vendor's statements, recommends updating following the security bulletins indicated in the references. There are dedicated pages for Password Manager Pro (CVE-2026-18199), for PAM360 and for two builds of SharePoint Manager Plus, 4507 and 4508.
Those who manage their own servers should have an orderly patching process. Automating server configuration with Ansible can help, and this also applies to urgent updates such as those for Linux from Fragnesia.
Limits to know
The source is a brief summary. It gives no CVSS scores, no CVE identifier for each flaw, and does not say which product suffers from which defect. It does not say whether there are active exploits, and we do not claim it. The technical detail is in the vendor's bulletins, which we could not read for this analysis.
What changes for those working in digital
If your company uses these products, the first step is to check the installed build and compare it with the list. If it is among those indicated, plan the update right away, because these are tools with access to sensitive credentials. Then check who can reach these systems from the network. If you manage servers for clients, notify them and document the intervention. Those who do not have time to follow patches can rely on hosting with managed servers and security updates.
Our take
The fact that weighs most is that two of the three products exist to protect access. A password manager is effective only if it is more secure than what it guards, and every flaw in this category is a potential incident across everything else. The ACN alert is useful but sparse, and a technical reader still has to open the bulletins. It remains a good example of how security depends on how fast you update, more than on the news itself.
Frequently asked questions
Which ManageEngine products are involved?
There are three – SharePoint Manager Plus, Password Manager Pro and PAM360. For each one the ACN lists the affected versions. If you use other ManageEngine products, this summary does not mention them.
What is the secure version of SharePoint Manager Plus?
Versions prior to 4508 are vulnerable. The vendor has published build 4508, cited in the alert's references. Update following the relevant bulletin.
Is the severity critical?
No, the ACN classifies it as high. The three vulnerabilities are rated high according to the summary. The source gives no numeric score.
Are there attacks in progress?
The source does not say. The alert mentions updates that fix the flaws, without citing active exploits. It is still advisable to update without waiting.
Where do I find the update instructions?
In the vendor bulletins linked by the ACN in the References section. There is one for Password Manager Pro, one for PAM360 and two for SharePoint Manager Plus.
What to check in the coming weeks on ManageEngine systems
After the update, the work is not finished. Verification and more precise information from the vendor are needed.
- Reread the vendor bulletins to understand which CVEs match each product.
- Check the access logs of Password Manager Pro and PAM360 for unusual activity prior to the patch.
- Consider changing the most sensitive credentials stored in the managers if the logs show anomalies.



