
 Ing. Calogero Bono
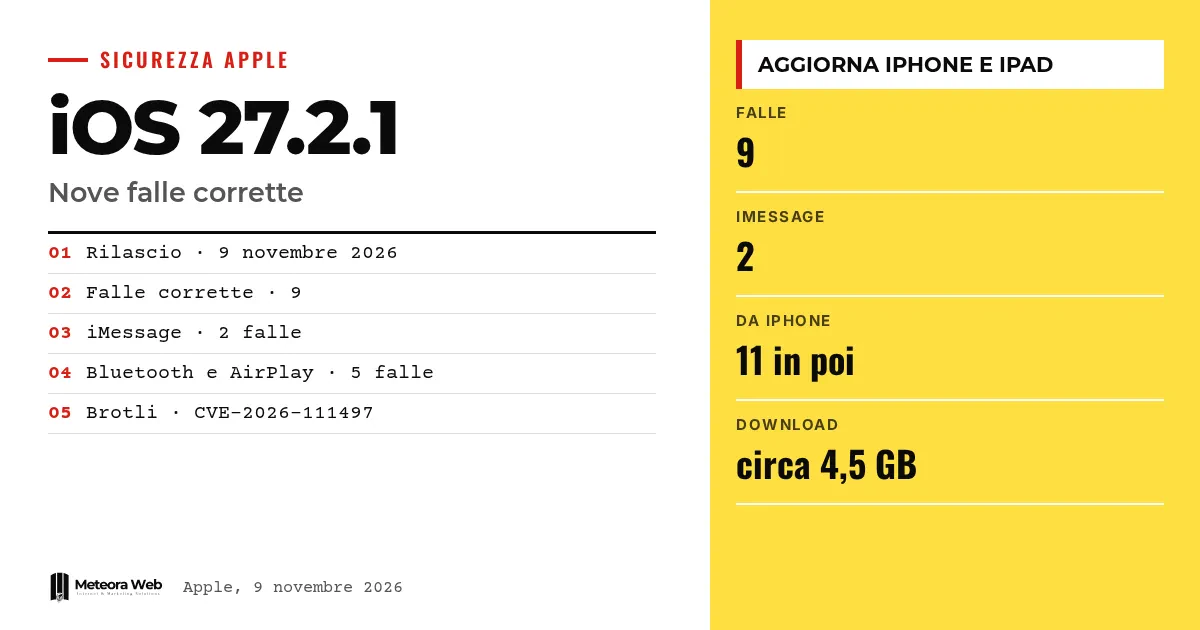
On November 9, 2026 Apple released iOS 27.2.1 and iPadOS 27.2.1, an update that looks minor in its short release notes but closes nine vulnerabilities on the security page. Two affect iMessage group chats, others touch Bluetooth and AirPlay pairing. It matters because some flaws required no action from the victim, and not all devices receive the same fixes.
A few terms before we get into the facts. CVE is the code that uniquely identifies a known vulnerability. Rate limit is the cap on repeated attempts, for example on a pairing code. Use-after-free is a memory error in which a program uses data that has already been released. Brotli is a compression library from Google. KEV is the catalog of actively exploited vulnerabilities kept by the US agency CISA.
What was fixed in iMessage?
According to Apple's security page, two flaws concern Messages. CVE-2026-113961 could allow a remote attacker to enter an iMessage group chat and receive messages. Apple describes an authorization problem, fixed with better validation.
CVE-2026-113960 instead concerns people added to a group, who could read messages sent before they joined. Apple fixed it by removing the vulnerable code. Both are credited to an anonymous researcher.
What changes for Bluetooth and AirPlay?
The pairing fixes are several. Two flaws in CoreUtils could allow pairing without user interaction, one from a malicious Bluetooth device and one from someone within radio range.
Two others allowed bypassing the attempt limit on the pairing code, one from Bluetooth proximity in AirPlay and one from the same network in rapportd. There is also a Bluetooth flaw that could corrupt a process's memory. As Punto Informatico explains, it is like trying every combination on a lock instead of stopping after a few mistakes.
Why is the Brotli flaw more delicate?
CVE-2026-111497 is an out-of-bounds write in Brotli which, with specially crafted input, could lead to memory corruption. According to The Hacker News, CISA added it to the catalog of exploited vulnerabilities on October 27.
Apple's notes do not mention attacks using this flaw. The data therefore comes from CISA, not Apple, and should be kept separate. CISA also notes that different products may use the same component.
Which devices and how to update?
The update is available for iPhone 11 and later and several iPads, from the 12.9-inch iPad Pro 4th generation to the iPad mini 6th generation. Go to Settings, General, Software Update. According to Punto Informatico the download is about 4.5 GB.
Other updates released the same day have separate notes. The iMessage and Brotli fixes do not appear in iOS 18.7.12 and watchOS 26.6.1, as The Hacker News reports. For the wider picture on other platforms, see our article on the November 9 security updates.
To go further, see iOS 27.3, Apple releases the first developer beta one week after 27.2 and iPhone Duo, Apple says over 100,000 apps are optimized and explains how to prepare.
Limits to know
Apple's notes do not say whether the iMessage flaws were exploited, what an attacker would need, whether members would see an intruder, or whether everyone must update to be protected. It is unclear what a paired device could do covertly. For iPhone XS, XS Max, XR, seventh-generation iPad and some Apple Watch models, the same fixes do not appear. Punto Informatico reports that Apple detected no real exploitation of the pairing flaws, but we did not find this on the official page.
What changes for those working in digital
If you use iMessage for work, with client or collaborator groups, update your iPhone and iPad right away and ask your team to do the same. The risk concerns the confidentiality of conversations that often contain business data. For older company devices that do not receive these fixes, consider whether to keep using them for sensitive communications. Anyone managing device fleets should check the installed versions. Developers should remember that Brotli is a widely used library, even outside the Apple world, and check whether their projects rely on it.
Our take
The release shows a communication problem. Short notes and no new features lead many to postpone, precisely when the update fixes flaws in private chats. Apple chose not to comment until it had the patches, which is a defensible choice. But it leaves those managing mixed fleets without answers while they must decide quickly. It would help to state clearly which models remain exposed and why. A detailed security page does not replace an explanation.
Frequently asked questions
When was iOS 27.2.1 released?
On November 9, 2026. It is meant for iPhone 11 and later and several iPad models. It brings no new features, only fixes.
How many vulnerabilities does it fix?
Nine, according to Punto Informatico. They concern Messages, Bluetooth, AirPlay, CoreUtils, rapportd, App Intents and Brotli.
Were the iMessage flaws exploited?
It is not stated. Apple's notes do not say so and do not explain what an attacker would need.
Is my iPhone XS protected?
It does not appear to be. According to The Hacker News, updates for iPhone XS, XS Max and XR do not list the iMessage fixes.
How do I install the update?
Go to Settings, General, Software Update. The download is about 4.5 GB according to Punto Informatico.
What to watch in the coming weeks on Apple patches
Open questions remain about older models and the real risk of the iMessage flaws. Apple's next notes may clarify them.
- Check whether updates arrive for iPhone XS and XR with the iMessage fixes.
- Follow the CISA catalog to see whether other Apple flaws are marked as exploited.
- Read the iOS 27.3 beta notes to understand which fixes will arrive next.
Sources
- support.apple.com
- thehackernews.com, Apple Patches iMessage Group Chat Privacy Flaws and Bluetooth Pairing Vulnerabilities
- punto-informatico.it, iOS 27.2.1 – 9 vulnerabilità risolte tra iMessage e Bluetooth, come scaricare l’update
- 9to5mac.com, iOS 27.2.1 has fixes for security issues in Messages, AirPlay, and more



