
 Ing. Calogero Bono
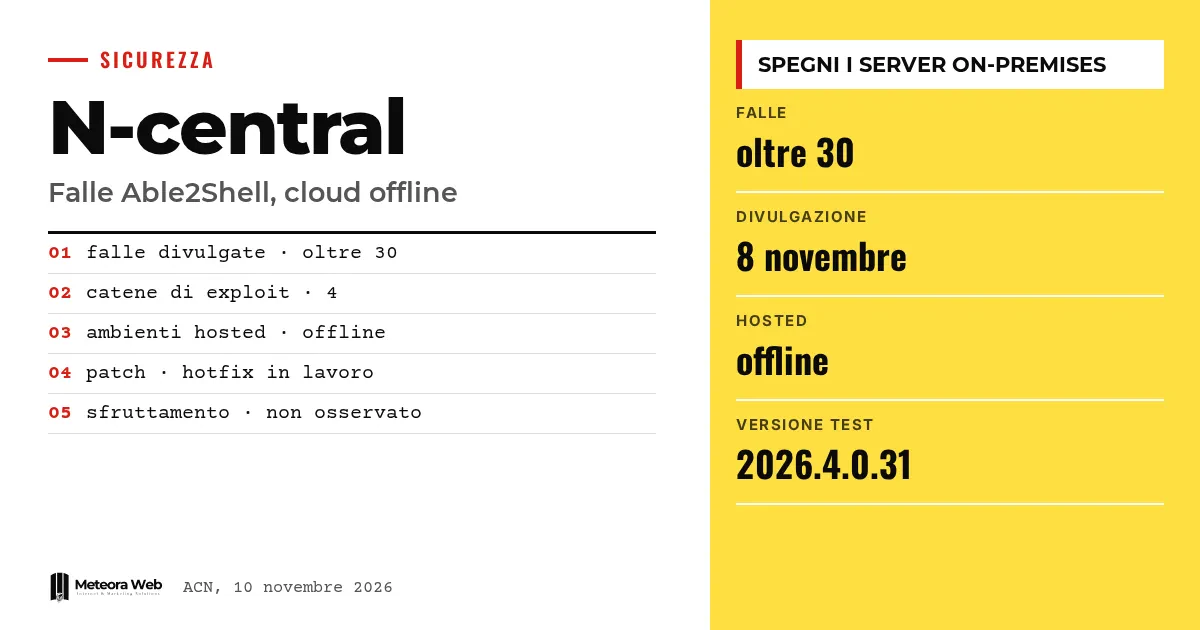
N-able has taken the hosted N-central environments offline and is asking on-premises customers to shut down their own servers. On November 9, after more than 30 0-day vulnerabilities called Able2Shell were published, the company declared a critical incident. ACN has also issued an alert. It matters because N-central is a platform used to remotely manage the devices of many IT companies' customers.
A few terms before we get into the facts. RMM is remote monitoring and management software for devices. A 0-day is a flaw that can be exploited before a fix exists. RCE means remote code execution. XXE is an attack that abuses XML files to read data or gain access. XSS injects malicious code into a web page that is then executed by the browser of whoever visits it.
What happened to N-central?
According to BleepingComputer, researcher Sean Bales disclosed the flaws on Sunday, November 8. He published a GitHub repository called Able2Shell with demonstration exploits.
N-able explained that it received a "non-responsible" disclosure of critical vulnerabilities found by an independent researcher. The following day it shut down the hosted environments in the Americas, Europe and Asia-Pacific, as also reported by The Hacker News.
What can the flaws allow?
The ACN alert describes an unauthenticated remote attacker who could bypass authentication, obtain credentials, alter configurations, write files and execute code with elevated privileges.
The agency describes four exploitation chains available online. One starts with a pre-authentication XXE, reaches a password reset and command execution as the nable user. Another turns a stored XSS in patch metadata into code execution with UID 0, that is root.
Which versions are affected?
ACN indicates N-central in both its hosted and on-premises variants. The causes are inadequate handling of user-supplied data, insufficient permission checks and improper separation between sessions, customers and devices.
Bales says he tested the exploits on version 2026.4.0.31, a pre-release, and believes almost all the flaws also affect earlier versions. This is his assessment, not confirmed by official sources.
What should customers do?
ACN recommends following the vendor's guidance and switching off on-premises servers until updates are released. If that is not possible, reachability can be limited to authorized networks and systems, including via VPN. The agency specifies that these measures do not guarantee complete mitigation.
The Ecoverse services accessible from N-able Login remain active, including Asset View, Patching and Vulnerability Management, says N-able. We saw a similar emergency with the zero-day on Cisco ASA and FTD SSL VPN.
Limits to know
BleepingComputer has not independently verified all the flaws, although the fix in preparation suggests at least some are real. N-able says it has not observed active exploitation or unauthorized access to data, but that is the company's own statement. There is no restoration date. Bales' claims about earlier reports being ignored remain to be confirmed, and the company has not responded on that point.
What changes for those working with digital systems
If you manage clients using N-central, for now you lose the tool you use to monitor and update their devices. You need a backup plan, for example the services indicated by the vendor, and a way to notify your clients. Check whether your on-premises server is reachable from the Internet, because a compromised remote management platform opens the way to every connected device. The case shows how much correct infrastructure configuration matters, and anyone using managed servers with security updates knows exposure must be kept to a minimum.
Our take
The case reveals two problems. The first is technical – tools with such broad privileges should be the most hardened, and the chains described by ACN point to weak controls. The second is procedural. Publishing exploits without warning is a choice that puts thousands of customers at risk, regardless of Bales' reasons. If his claims are true, however, N-able would have ignored precisely the channel meant to prevent these situations. We should wait for the facts before blaming one party alone.
Frequently asked questions
What is Able2Shell?
It is the collective name for over 30 0-day vulnerabilities in N-central disclosed by Sean Bales. The name is also that of the GitHub repository with the demonstration exploits.
Is N-central still available?
No, the hosted environments are offline. N-able asks on-premises customers to keep their servers switched off until further notice.
Are there attacks in progress?
N-able says it has not observed active exploitation. ACN, however, reports that exploitation chains are available online, so the risk remains.
Is there a patch?
Not yet. N-able is developing and validating a hotfix, with no release date.
What can I do if I cannot switch off the server?
Limit access to authorized networks and systems, including via VPN. ACN warns that this is not enough to fully mitigate the flaws.
What to watch for in the coming days on N-central
The key point now is to find out when the hotfix arrives and whether signs of real attacks emerge. N-able promises updates every four hours.
- Follow N-able's status updates and ACN's communications before turning any server back on.
- After the patch, check administrative accounts and logs to verify that no users were created without authorization.
- Watch whether the disclosure of N-able's other flaws, still unresolved according to Bales, will follow.



