
 Ing. Calogero Bono
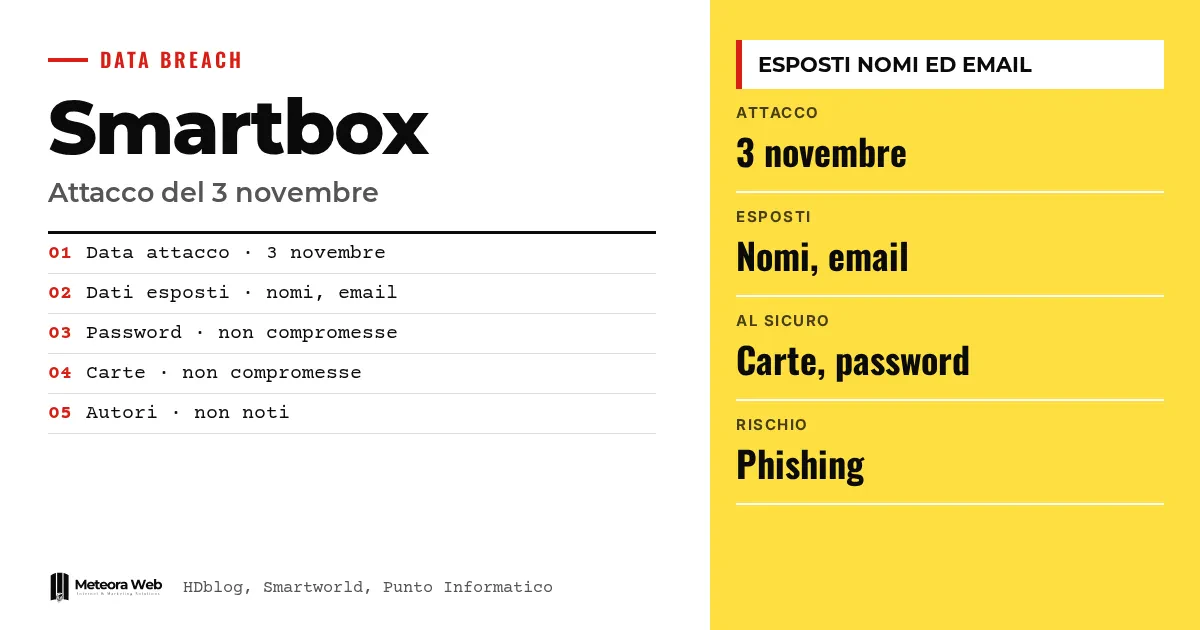
Smartbox, the company behind gift experience boxes, has emailed its customers about a security incident that took place on November 3. Someone gained unauthorized access to one of the company's platforms. According to the sources, names and email addresses are exposed, while passwords and payment card data do not appear to have been touched. This matters because that kind of data can be used to craft very convincing phishing messages.
A few terms before we get into the facts. Unauthorized access means someone has entered a system without having the right to do so. Phishing is the fake email that imitates a real company to get you to hand over passwords or payment details. Two-factor authentication adds a second check beyond the password, such as a code sent to your phone. The Italian Data Protection Authority (Garante per la protezione dei dati) is the authority that oversees the processing of personal data and receives reports of breaches.
What happened at Smartbox on November 3?
Platform users received an email titled «Communication about a data security incident», sent from info@serv.smartbox.com. This is reported by HDblog, whose author received it on November 7, four days after the breach.
The text describes unauthorized access in general terms. It does not clarify who carried it out or how. The company says it has taken the necessary steps to prevent it from happening again.
Which data was exposed and which was not?
According to what Smartbox has stated, and as reported by Smartworld, internal investigations indicate that customers' names and email addresses may have been exposed. Account passwords and payment card data would not have been compromised.
This is the company's statement, not an independent verification. Punto Informatico confirms the same picture, with personal data such as names and emails and no theft of cards or passwords.
Why is phishing the real risk?
With a name and email address, whoever carried out the attack can write targeted messages posing as Smartbox or other services. Smartbox warns not to click suspicious links and reminds customers that it will never ask for a password or card details by email.
One useful detail. According to Punto Informatico, users will receive a new confirmation code for gift boxes by email. If a message asks for a password or payment details, it is certainly phishing. To learn how to recognize it, we wrote a guide on phishing and email scams in the workplace.
Who is behind the attack?
Nobody knows. Punto Informatico notes that the perpetrators of the Smartbox intrusion are not known and places the case in a broader context of attacks attributed to Russian cybercriminals, such as the one on the company Bbt Se that manages the Brenner tunnel. In that case, the first investigations point to the Everest group.
Nothing links the two episodes. The general picture is still useful, as the case of the refrigerators of the French blood bank also shows.
Limits to know
There are gaps in what we know about who carried out the attack, how they did it, and how many customers are affected. Everything we know about exposed and protected data comes from the company, and the investigation is still ongoing. The sources also disagree on a minor point – Smartworld gives the date as November 3, 2026, while the others only say November 3. The picture may change with new statements.
What changes for people who work with digital tools
If you are a Smartbox customer, treat any email or message that mentions gift boxes, bookings or accounts with suspicion. Do not click the links and do not enter passwords or card details. If you use the same password on several services, change it now and turn on two-factor authentication. Business owners have one more rule to follow. A list of customers with names and emails is a target, so it is worth knowing where it is stored and who can access it. Even a breach without stolen passwords can turn into spear phishing.
Our take
Smartbox's notice arrived four days after the events, at least in the case reported by HDblog, and it is vague about causes and methods. Reassuring customers about cards is right, but saying little about how the access happened leaves customers with nothing to judge the risk by. Names and emails may seem like minor data, but they are the fuel of phishing. Anyone who collects customer data should treat it as an asset to protect, not as a detail.
Frequently asked questions
When did the Smartbox attack happen?
On November 3. The email notice reached customers over the weekend, and in the case reported by HDblog it arrived on November 7.
Which Smartbox data was exposed?
Customers' names and email addresses. According to the company, account passwords and payment card data were not compromised.
Do I need to change my Smartbox password?
It is not required, since the company says passwords were not touched. Changing it is still a prudent choice, especially if you use it elsewhere. It is better to have a different password for each service.
How do I recognize a fake Smartbox email?
Be wary of any message asking for passwords or payment details. Smartbox states it will never ask for them by email. Avoid suspicious links.
Who carried out the Smartbox attack?
It is not known. Punto Informatico writes that the perpetrators are unknown, and there is no confirmed link to other recent attacks.
What to watch for in the coming weeks in the Smartbox case
The investigation is open and little information is available so far. In the coming days it is wise to follow official updates and stay alert to your inbox.
- Check whether Smartbox publishes updates on the perpetrators, methods and number of customers involved.
- Make sure the new confirmation code for gift boxes arrives only from the company's official channels.
- Consider a password manager to use unique credentials, but first read this article on password manager vulnerabilities.
Sources
- hdblog.it, Smartbox ha subito un attacco – l'avviso via email, cosa fare con le prenotazioni
- smartworld.it, Smartbox, attacco informatico del 3 novembre – esposti nomi ed email dei clienti, ma password e carte sono al sicuro
- punto-informatico.it, Guerra ibrida – attacco al tunnel del Brennero e Smartbox



